Every South African business eventually faces the same uncomfortable question.
If your primary systems failed tomorrow morning, how long would it take to get back to work—and how much would you lose in the meantime?
The answer depends almost entirely on the backup solutions you have in place and where those backups live. The debate between cloud and on-premises backup is often framed as a technology decision. In practice, it’s a risk decision. Each approach protects well against certain failure scenarios and poorly against others.
What On-Premises Backup Actually Means
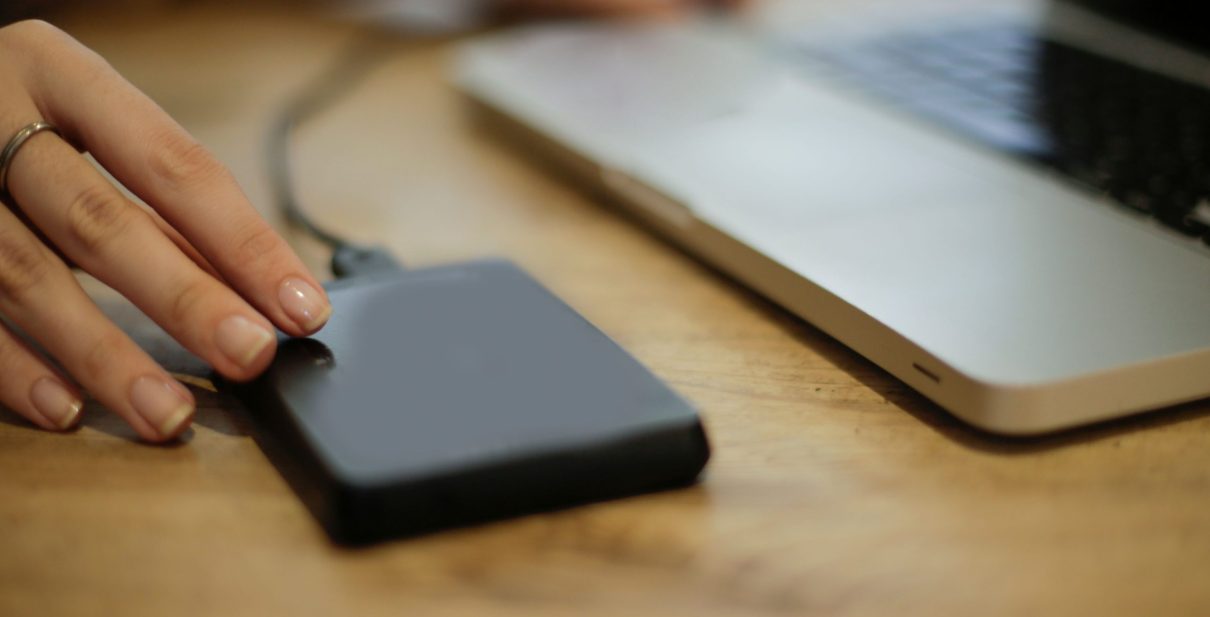
On-premises backup stores copies of your data on hardware you own and control, physically located at your business premises. This typically involves a network-attached storage (NAS) device, a dedicated backup server, external drives, or in larger environments, tape libraries.
Backup software runs on a schedule, copying data from your production systems to this local storage. When you need to restore a file, a folder, or an entire server, you pull it back across your local network.
The appeal is immediate: you own the hardware, the data never leaves your building, and restoration happens at local network speed rather than depending on your internet connection.
What Cloud Backup Actually Means
Cloud backup sends encrypted copies of your data across the internet to secure data centres operated by a backup provider. The provider handles the infrastructure — the servers, the storage arrays, the power redundancy, the physical security, the hardware refresh cycles — and you pay a subscription based on the volume of data you’re protecting.
Modern cloud backup runs continuously or on frequent schedules, encrypts data before it leaves your premises, and makes restoration possible from anywhere with an internet connection.
The appeal is equally clear: no capital outlay, no hardware to maintain, and geographic separation between your business and your backups.
Where On-Premise Backup Wins
Restoration speed is the strongest argument for local backup. If a server fails and you need to restore two terabytes of data, pulling that across a local gigabit network takes a few hours. Downloading the same volume over a 100 Mbps fibre line takes considerably longer, assuming you have the full line available and nothing else competing for bandwidth.
For businesses with large datasets and tight recovery time requirements, this difference matters enormously.
No bandwidth dependency means your backup and restore operations don’t compete with daily business traffic. A business running design files, video production, CAD drawings, or large databases can back up hundreds of gigabytes daily without saturating an internet connection that staff also need for everything else.
Predictable costs after initial investment. Once you’ve bought the hardware, your ongoing costs are electricity, occasional drive replacements, and your time. There’s no per-gigabyte subscription that grows as your data grows.
Full control over the data. For businesses with specific contractual or regulatory obligations about where data resides and who can physically access it, on-premise storage answers those questions definitively.
Where On-Premise Backup Fails
Site-level disasters destroy everything at once. Fire, flooding, burst geysers, load shedding and burglary don’t distinguish between your production server and the backup NAS sitting on the shelf beside it. A break-in that takes your server cabinet takes your backups too. In a South African context, where business premises burglary remains a real and common risk, this isn’t theoretical.
Ransomware actively hunts connected backups. Modern ransomware variants are specifically written to locate network shares, mapped drives, and backup repositories, then encrypt or delete them before encrypting production data. A backup NAS permanently mounted to your network is a target, not a safeguard.
Load shedding damages hardware. Repeated power cycling stresses drives and controllers. Businesses running backup hardware without adequate UPS protection frequently discover drive failures or corrupted backup catalogues at exactly the moment they need to restore.
Hardware ages and fails. Drives have finite lifespans. RAID arrays degrade. Backup hardware needs monitoring, testing, and eventual replacement—and in businesses without dedicated IT staff, that maintenance often quietly stops until something breaks.
Where Cloud Backup Wins
Geographic separation is built in. Your backups sit in a hardened data centre kilometres away from your premises, with redundant power, climate control, and physical security that far exceed what a typical SME could implement. A fire at your office won’t affect your backup copies.
Immutability defeats ransomware. Quality cloud backup providers offer immutable or versioned storage, where backup copies cannot be altered or deleted for a defined retention period—even by someone with valid administrator credentials. This is currently the single most effective technical defence against ransomware destroying your ability to recover.
Automatic, hands-off operation. Once configured, cloud backup runs without human intervention, with alerting when jobs fail. No tape to swap, no drive to rotate offsite, and no reliance on someone remembering to do something every Friday.
Scales without capital expenditure. As your data grows, your storage grows. There’s no forklift upgrade when the NAS fills up, no procurement cycle, no capital approval process.
Restoration from anywhere. If your office is inaccessible, staff can restore critical files from home or an alternative site. During extended disruption, this flexibility keeps the business functioning.
Where Cloud Backup Struggles
Initial seeding takes time. The first full backup of a large dataset can take days or weeks over typical business internet connections. Most reputable providers offer physical seeding — shipping a drive — but this adds complexity to onboarding.
Large-scale restoration is bandwidth-bound. Recovering an entire server or file share over the internet is meaningfully slower than local restoration. Businesses with strict recovery time objectives need to account for this honestly rather than assuming cloud restoration is instant.
Ongoing subscription costs accumulate. Over a five-year horizon, cloud backup subscriptions for a large dataset may exceed the cost of owning hardware. The trade-off is that you’re also buying redundancy, security, and management you’d otherwise have to provide yourself.
Internet dependency. No connection means no backup and no restoration. Businesses in areas with unreliable connectivity need backup internet to make cloud backup dependable.
Data sovereignty questions. Under POPIA, businesses remain accountable for personal information regardless of where it’s processed. Cross-border transfers are permitted under specific conditions, but you need to know where your provider stores data and be able to explain that to a regulator if asked.
The Honest Answer: Use Both
The cloud-versus-on-premises framing creates a false choice. The approach that actually protects businesses is a hybrid one, and it maps directly onto the well-established 3-2-1 principle: three copies of your data, on two different media types, with one copy offsite.
A practical hybrid implementation looks like this:
Local backup handles the everyday cases — the accidentally deleted folder, the corrupted database, the file someone overwrote on Tuesday. These restorations happen in minutes because the data is right there on your network.
Cloud backup handles the catastrophic cases — the fire, the burglary, the ransomware event, the flood. These restorations are slower, but they’re the difference between a difficult week and the end of the business.
Critically, the cloud copy should be configured with immutability and should not be reachable with the same credentials that administer your local environment. If an attacker who compromises your domain administrator account can also delete your cloud backups, you don’t have a second line of defence — you have one line of defence with two copies.
Testing: The Step Almost Everyone Skips
Whichever architecture you choose, untested backups are not backups. They’re an assumption.
Failure modes are mundane and common: a backup job that has been silently failing for four months, a retention policy that expired the version you needed, a backup that completes successfully but excludes a critical database because it was locked at runtime, or an encryption key nobody documented.
Effective data recovery depends on verification, not configuration. Schedule genuine test restorations quarterly. Restore a real file, a real folder, and at least annually, a full system to alternative hardware or a virtual machine. Time each restoration and compare it against what your business can actually tolerate.
If a full restore takes eleven hours and your business can only absorb four hours of downtime, you’ve learned something valuable — and you’ve learned it on a Tuesday afternoon rather than during an actual crisis.
Matching the Approach to Your Business
Smaller businesses with modest data volumes and no dedicated IT staff are generally better served by cloud-first backup solutions with a light local component. The management overhead of on-premises infrastructure rarely justifies itself at this scale.
Mid-sized businesses with substantial datasets and meaningful downtime costs benefit most clearly from genuine hybrid architecture, where local speed and cloud resilience each do what they do best.
Businesses with regulatory constraints on data location, very large datasets, or exceptionally tight recovery time objectives may weight on-premises more heavily — but should still maintain an offsite copy, whether that’s cloud-based or a physically separate second site.
Getting It Right
Your goal isn’t to choose between approaches; it’s to pick the one that best protects your business. It’s which combination protects you against the specific ways your business could lose data — and whether you’ve actually tested that it works.
Kinetix Group helps South African businesses design and implement backup solutions that account for local realities: load shedding, connectivity variability, physical security risk, and POPIA obligations. We assess your actual recovery requirements, design appropriate architecture, and — critically — verify that data recovery works before you need it.
Get in touch for a backup assessment that tells you honestly where you stand.